Deployment
Fully managed SaaS or customer-hosted. Isolated tenant architecture, with customer-selected SIEM and EDR connections.
C7PLATFORM · Threat-informed defense for CTEM
Starting from Cyber Threat Intelligence (CTI), validate defenses, hunt for threats, and turn findings into detection and response as code.
European-developed, Belgium-based. SaaS or customer-hosted.
C7PLATFORM
Cyber Threat Intelligence is the starting point. C7PLATFORM turns what is known about adversary behavior into attack simulations, detection validation, guided hunts, and action on findings.
See It in Action
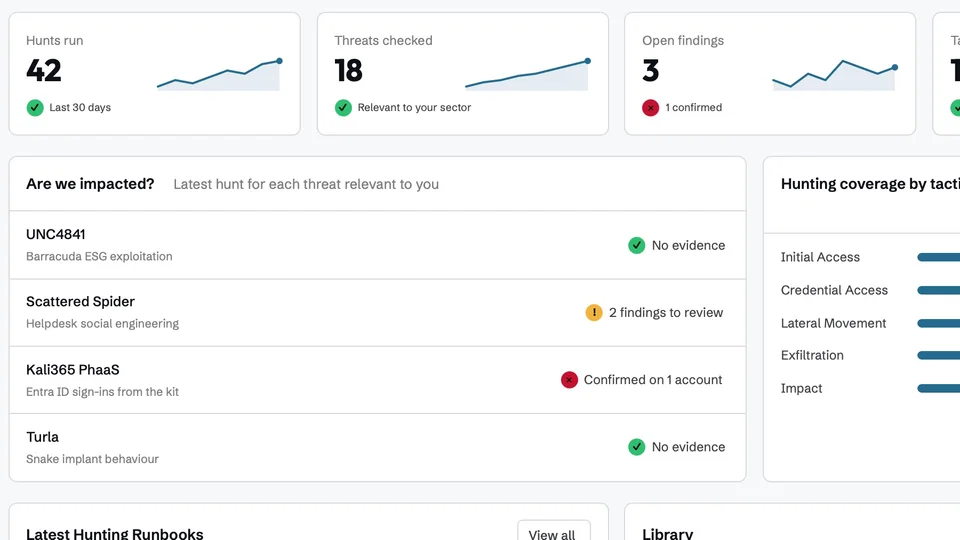
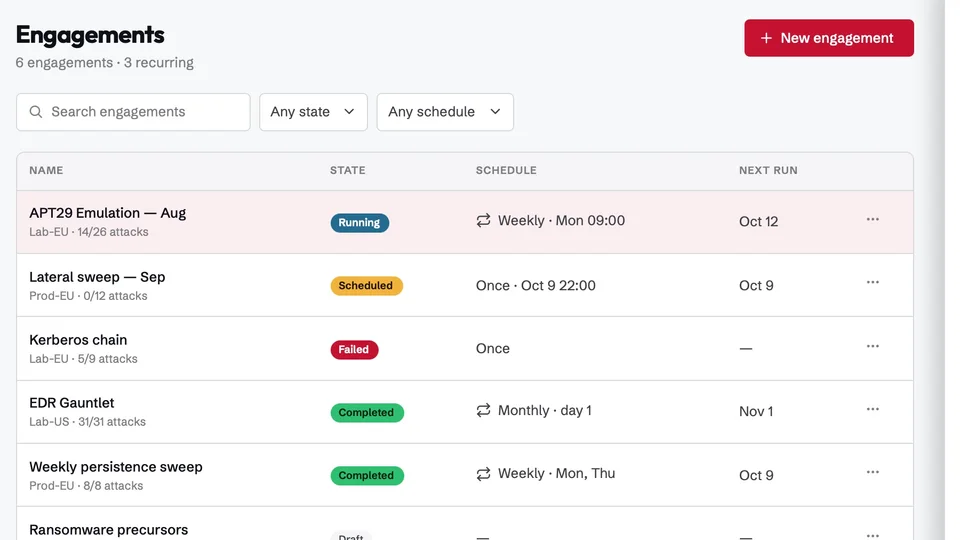
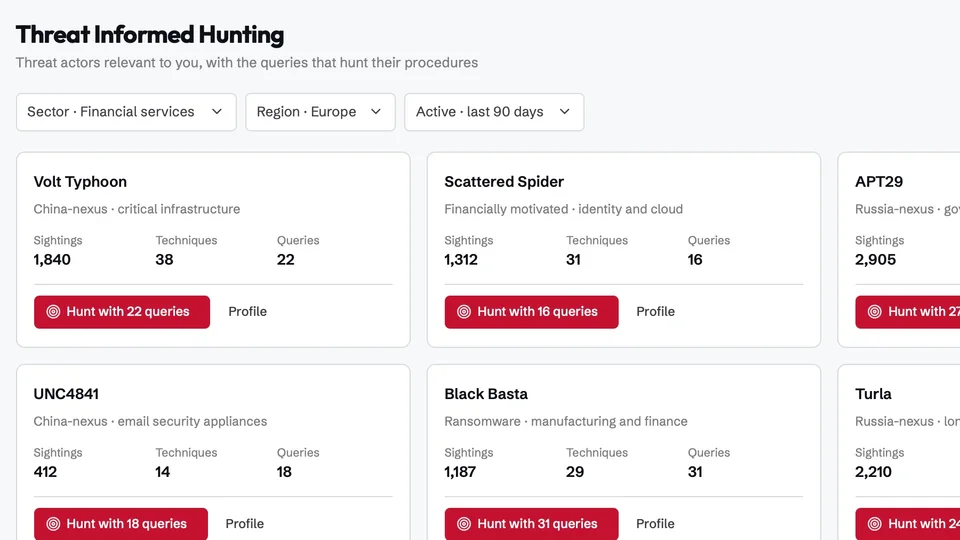
Explore attack execution, detection outcomes and guided threat hunts.
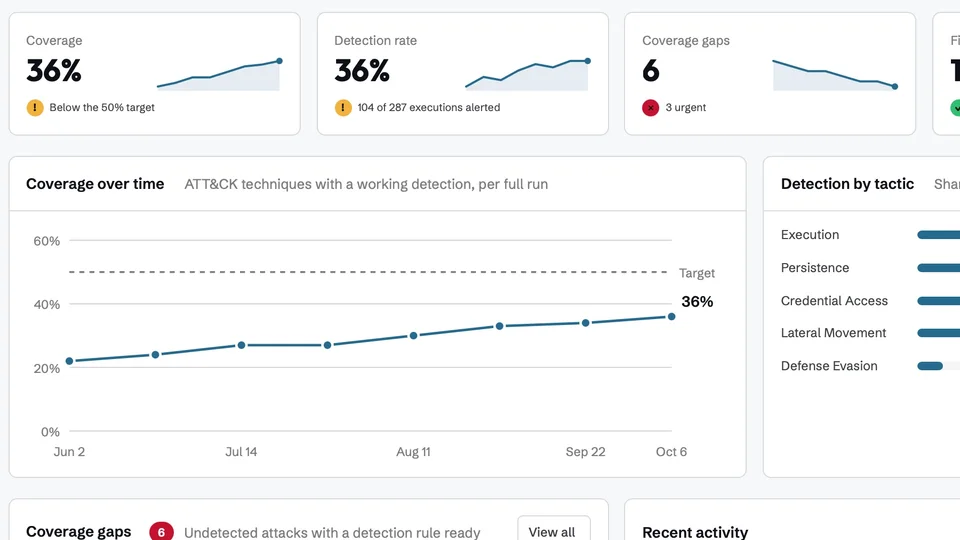
Coverage, detection rate and open gaps after every run, per ATT&CK tactic.
Two Products. One Platform.
C7ATTACK (HackerFlow) validates your defenses. C7DEFEND (7Hunter) searches for threats that got through. Explore the product behind each question.


Your CTEM Program
With adversarial exposure validation at its core, Crimson7 helps operationalize validation and supports mobilization within your CTEM program.
Built for Controlled Environments
Fully managed SaaS or customer-hosted. Isolated tenant architecture, with customer-selected SIEM and EDR connections.
Single sign-on, role-based access control, and full user activity and system audit logging.
Guardrails and outcome validation. No training on customer data. Connect customer-owned LLMs over an OpenAI-compatible interface, inside your environment.
European Sovereignty
Crimson7 is European-developed and Belgium-based. The platform is built for organisations that have to answer where their security data lives and who can reach it.
Licensing
C7ATTACK and C7DEFEND ship in three tiers. Start with Community for learning and research, run Enterprise against your own environment, or partner with us as a Service Provider. Every tier runs as SaaS or customer-hosted.
On application
For students, educators, and researchers. Learn on real community playbooks and attack scenarios, with limited seats. Access is granted on application.
Price on request
For direct customers managing their own environment, or that prefer we manage it for them. Full features with unlimited seats.
Price on request
For MSSPs, MDRs, MSPs, and managed security teams serving multiple clients.
Book a demo
Book a 30 minute demo. We run real threat hunting runbooks and attack playbooks on a working environment while you watch, so you can see what fires, what stays silent, and what it takes to close the gap.