01 / Services
Offensive Engineering
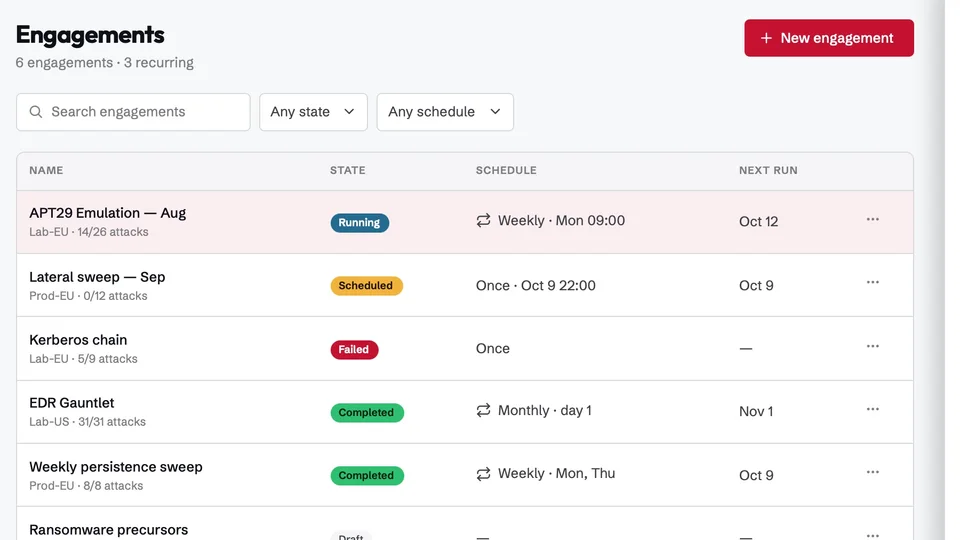
Red team, purple team, and adversary simulation that put your defenses under real, research-led pressure.



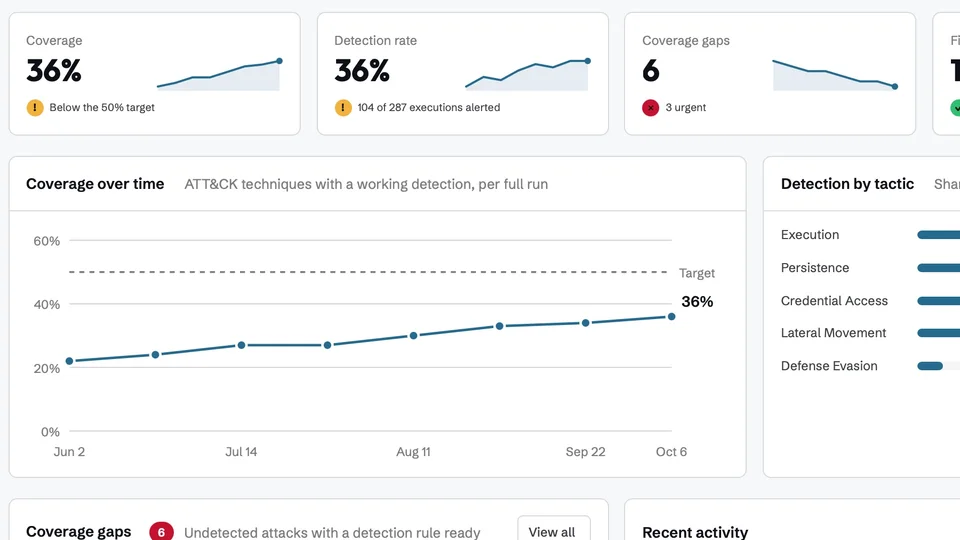
Coverage, detection rate and open gaps after every run, per ATT&CK tactic.
C7 Platform
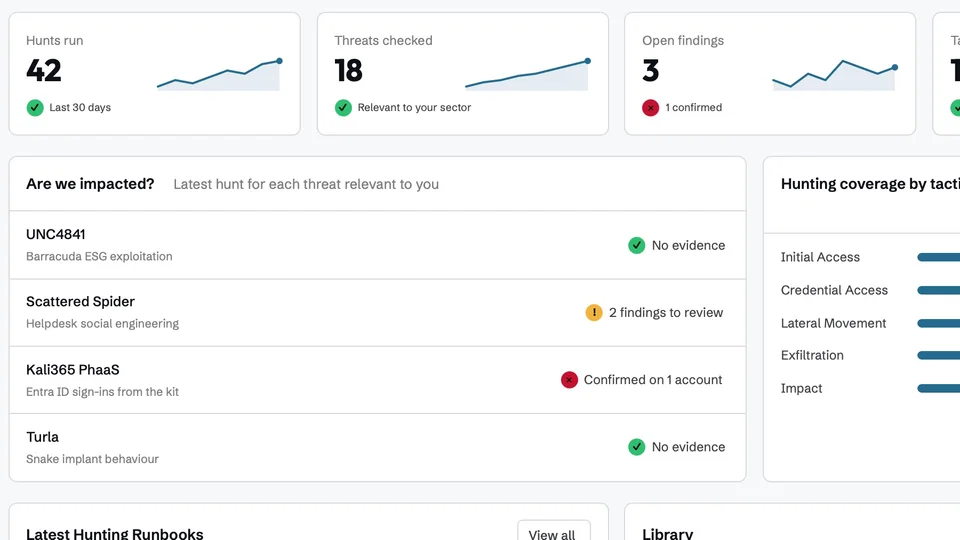
The same adversary research that powers our services is built into the platform: simulate attacks, prove detections, hunt, and remediate, end to end.
Validation and action for your CTEM program
Starting from Cyber Threat Intelligence, C7 Platform helps operationalize validation and supports mobilization in your CTEM program: simulate adversary behavior, prove how defenses respond, and turn findings into detection and response as code.
Adversarial Exposure Validation (AEV) is a core capability. Crimson7 carries validation into action with detection and response as code, re-tested against real adversary behavior.
Services
Our engineers run the platform with you and around you, from offensive testing to detection engineering to always-on managed programs.
Red team, purple team, and adversary simulation that put your defenses under real, research-led pressure.
Detection engineering, validation, and threat hunting that turn coverage gaps into measurable detections.
Purple Rain: continuous purple teaming delivered as an always-on managed program, not a tool license.
Hardware, firmware, IoT, ICS, and physical security testing for high-assurance and targeted environments.
Impact & Results
Identify and close the gaps that matter most, based on how real attackers would exploit them.
Get operational detection rules faster, delivered as code from real attack simulations, not theoretical analysis.
Meet TIBER, DORA, and other regulatory requirements with intelligence-led testing that actually improves security.
Give your security operations team better tools, better rules, and better understanding of the threats they face.