White-label
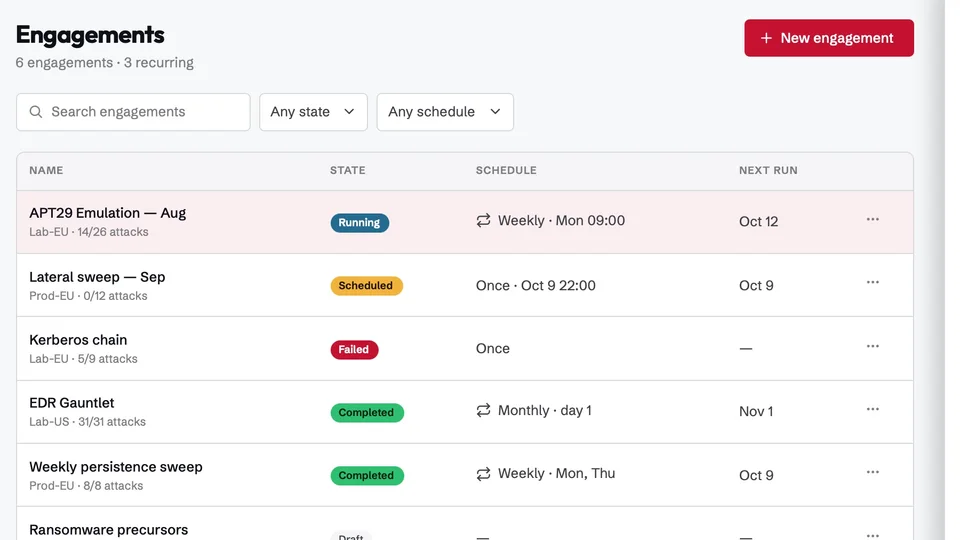
Isolated tenant per client, central multi-tenant management, and white-labelled reporting under your own brand.



The Operational Gap
The Model
Isolated tenant per client, central multi-tenant management, and white-labelled reporting under your own brand.
Fully managed SaaS or partner-hosted, with client-selected SIEM and EDR connections per tenant.
Single sign-on, role-based access control per tenant, and full user activity and system audit logging.
C7 Platform
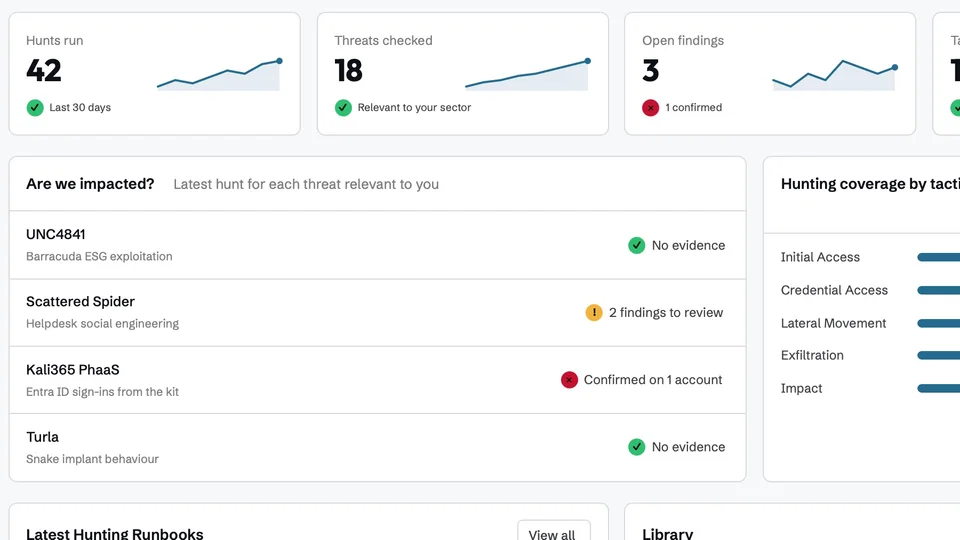
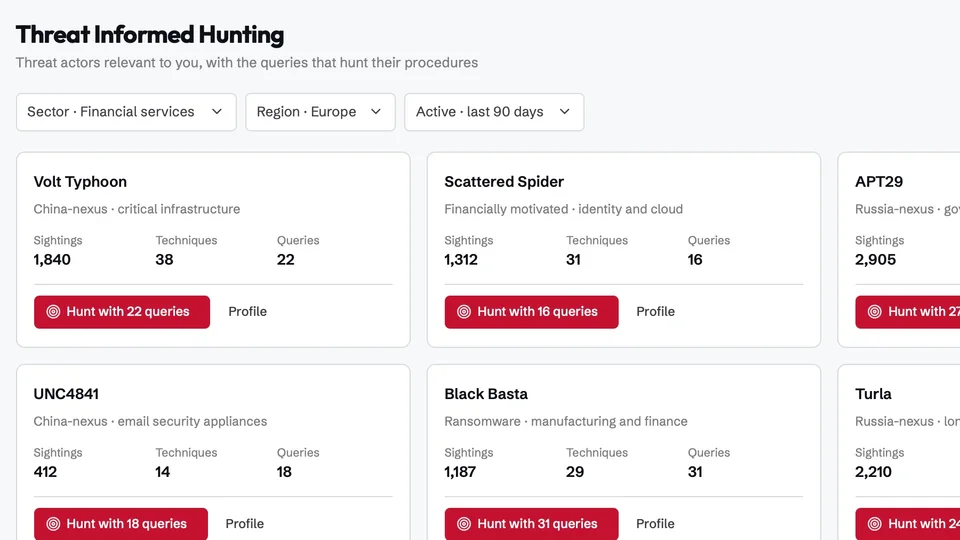
The same adversary research that powers our services is built into the platform: simulate attacks, prove detections, hunt, and remediate, end to end.
What Your Clients Get From You
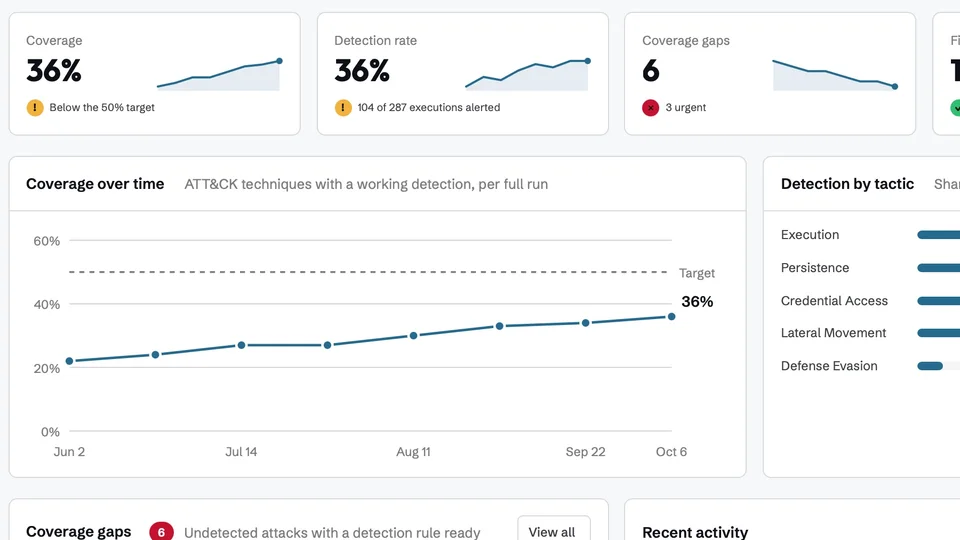
Attack-to-alert correlation shows which detections fired, which stayed silent, and what changed after remediation.
MITRE ATT&CK coverage reporting per tenant, so every engagement ends with a defensible picture of where they stand.
Hunts, investigations and validation results delivered white-labelled under your own brand.
Partner Licensing
No seat counting, no feature gates, no per-scenario billing. Your first managed tenant is included in the base licence, and the per-tenant rate drops as your portfolio grows. C7 Attack and C7 Hunt can be licensed separately or together.
Talk pricingBook a demo
Thirty minutes with the team. We run C7 Attack and C7 Hunt against scenarios that match the clients you serve, not a canned dataset.