Our Reason for Existence
To defeat APTs by using their own tradecraft against them.
Crimson7 exists to stop Advanced Persistent Threat (APT) actors by using their own tradecraft and Cyber Threat Intelligence (CTI) against them. We defeat APTs by increasing the cost of their activities and their ongoing, high-value campaigns targeting your digital assets. We raise the bar of your defences by fusing advanced research in detection and response, red team training of your blue teams, and our offensive security knowledge of tactics, techniques and procedures.
Defeating the attacker means knowing where their campaign will move to next. Crimson7's detection model is effective through the simplicity of its design: raise the cost of every move within a system by engineering effective detection rules, increasing what an attacker must spend on their next campaign step, until the detection fidelity of your defender systems defeats the entire campaign.
To anticipate is to prevail. Praevenire est vincere.
Category Positioning
From validation to action in your CTEM program
Continuous Threat Exposure Management (CTEM) spans scoping, discovery, prioritization, validation and mobilization. Crimson7 focuses on proving how your defenses respond to real adversary behavior and helping your team act on the results. Adversarial Exposure Validation (AEV) is a core capability within that contribution.
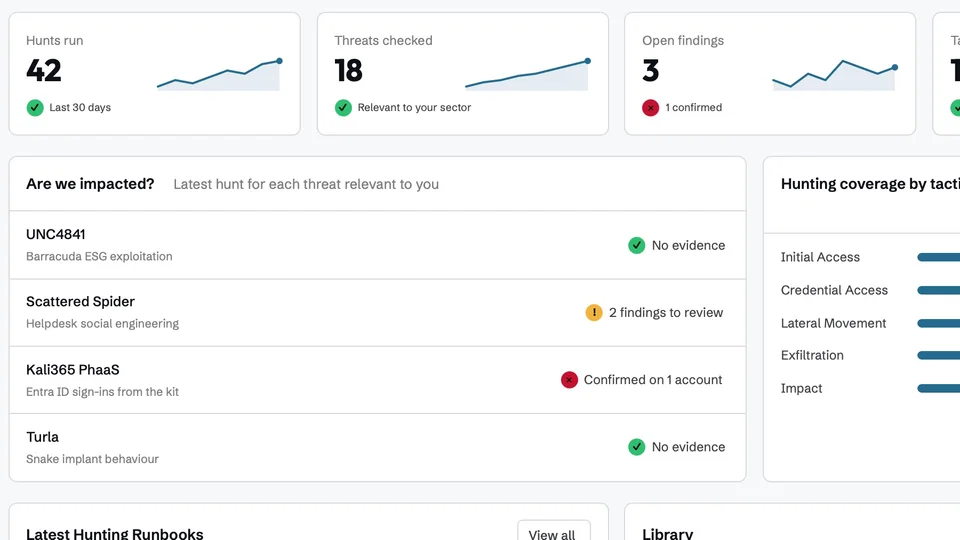
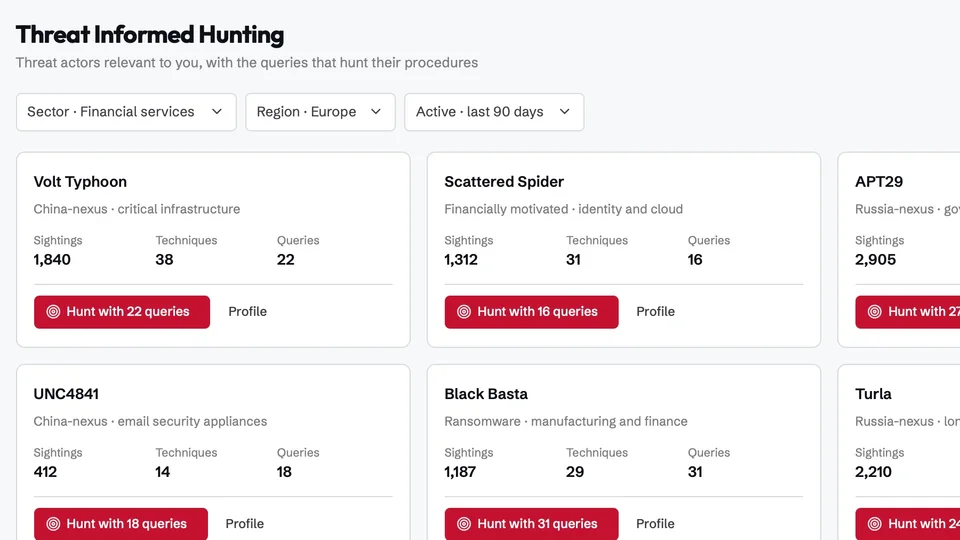
We call our approach CAEVR: Continuous Adversarial Exposure Validation and Remediation. Validate continuously at the Speed of Threat, hunt for threats that got through, and turn findings into detection-as-code and response-as-code, engineered and tested through Detection Engineering and Validation (DEV).
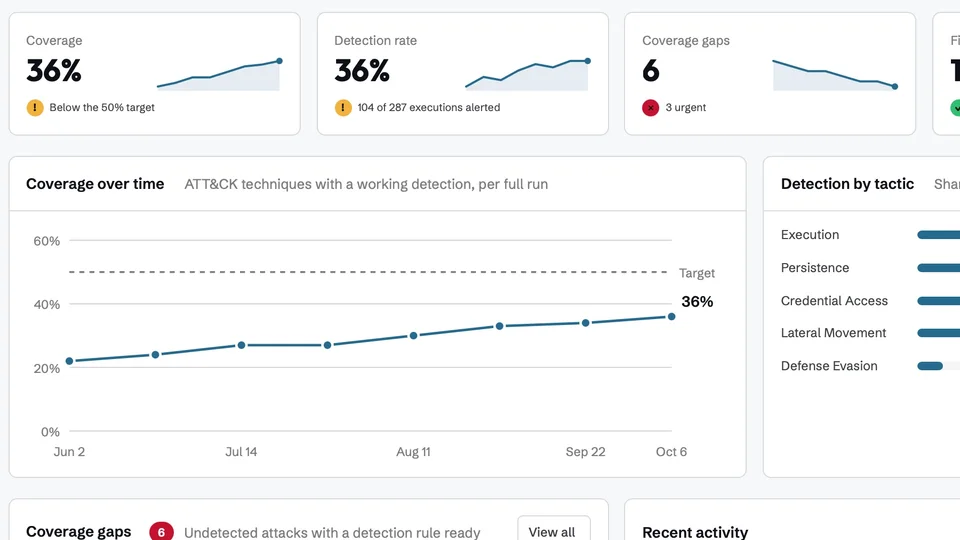
Crimson7 supports your CTEM program by operationalizing validation and supporting mobilization. C7ATTACK validates defenses against real adversary techniques. C7DEFEND investigates current and historical data. Our engineering services help teams turn findings into operational detection and response.
The Differentiation
The answer to 'and now what?'
Most security validation programs answer 'what are you exposed to?' Crimson7 answers how good your current detections are at stopping active APT campaigns, and makes your future actions better. We provide Actionable, Contextual and Timely (ACT) detection rules and key response actions that you can test and deploy immediately into your security stack.
See It Live
Watch us run real adversary techniques against live defences
The session is postponed and a new date is being set. Nick Maeckelberghe opens with who we are and why we exist, then Joey Verleg runs C7ATTACK and C7DEFEND live: attack execution, detection outcome, and detection-as-code remediation in a single hour. Sign up and we will email you the date as soon as it is confirmed.
Get notified about the webinarBook a demo
Ready to validate your detections?
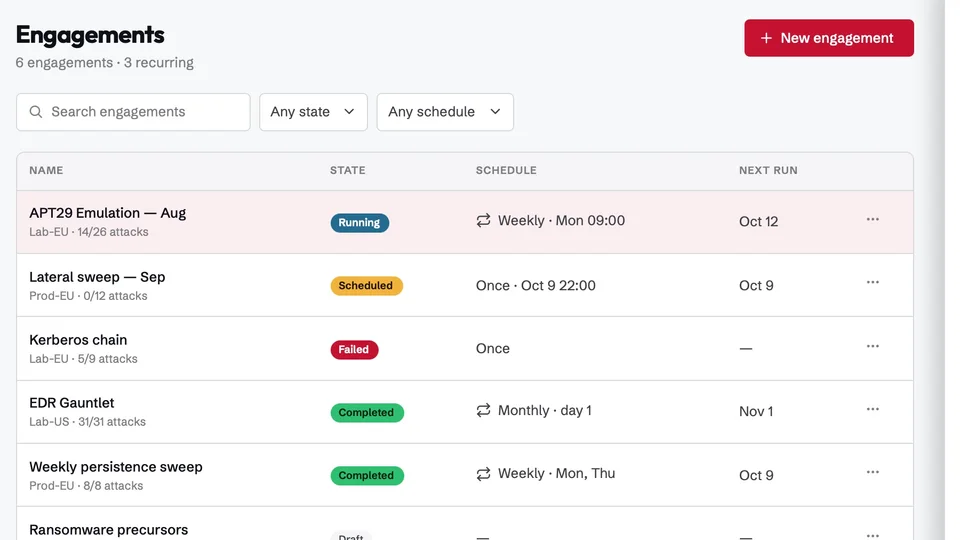
Book a demo of C7ATTACK. We run real attack techniques on a working environment, show you exactly what fires and what stays silent, and walk through the ACT detections that close the gaps.