Attack Simulation is Too Complex
Most simulation tools can't execute modern in-memory attacks or emulate sophisticated C2 infrastructure. They simulate the easy stuff and miss what APTs actually do.
How it works
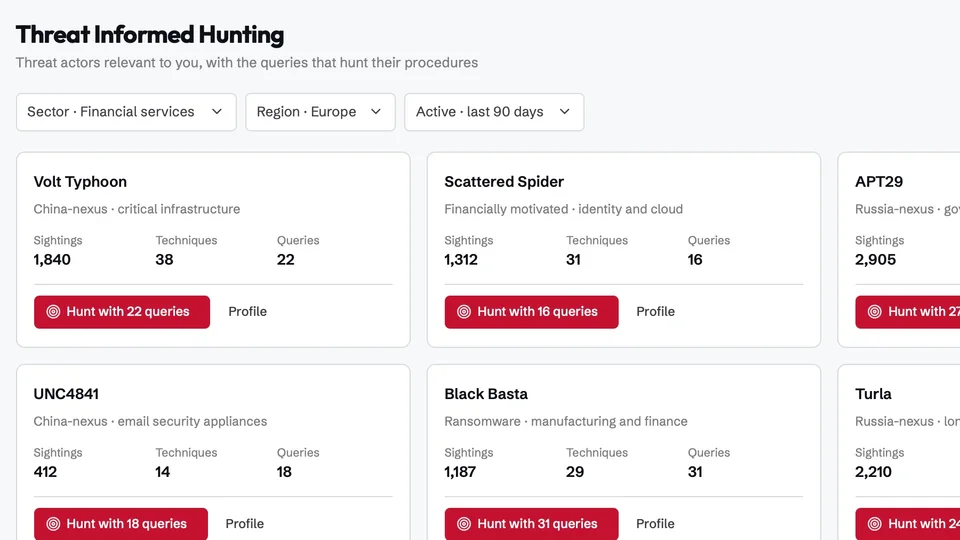
Five stages, each in the product: pick the adversary, run the attack, read the results, ship the fix and prove it fires.
Ingest threat actor profiles and map known behaviours to your environment.
Develop custom TTPs from breach analysis and malware reverse engineering.
Continuous loop: results feed back into intel
Book a demo
In 30 minutes an engineer runs C7 Attack on a working environment and answers your questions on deployment, integrations and licensing. What we cover:
The Problem
Most simulation tools can't execute modern in-memory attacks or emulate sophisticated C2 infrastructure. They simulate the easy stuff and miss what APTs actually do.
Without continuous validation against your actual defenses, security teams can't tell which threats are detected and which sail straight through your controls.
Legacy validation platforms lack proper result parsing, AI integration, and end-to-end Purple Team support, leaving operators with raw data and no actionable output.
The Solution
C7 Attack is designed for consulting firms and security teams that run continuous Purple Team programs. Licensed for client delivery, it combines automated attack execution with human operator control, giving you the depth of a real engagement at the speed of automation. Available as SaaS or customer-hosted.
Runs as fully managed SaaS or customer-hosted, with customer-selected SIEM and EDR connections. See how the platform runs in controlled environments.
Capabilities
Emulate how the actor actually operates, not a signature or an IOC replay.
Fileless payloads and real command-and-control behaviour, including techniques most tools cannot reach.
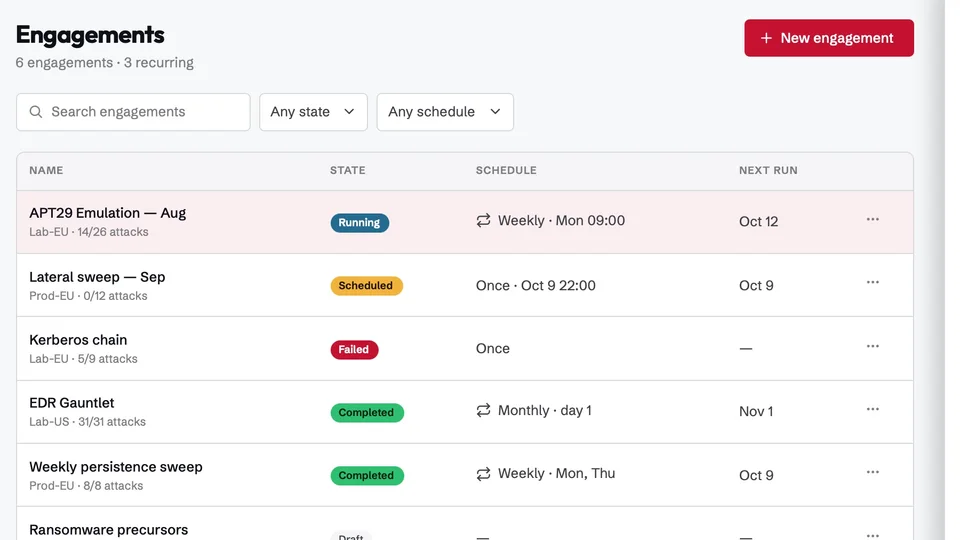
Automation removes the toil, the operator keeps the judgement. Engagement-grade depth at the speed of automation.
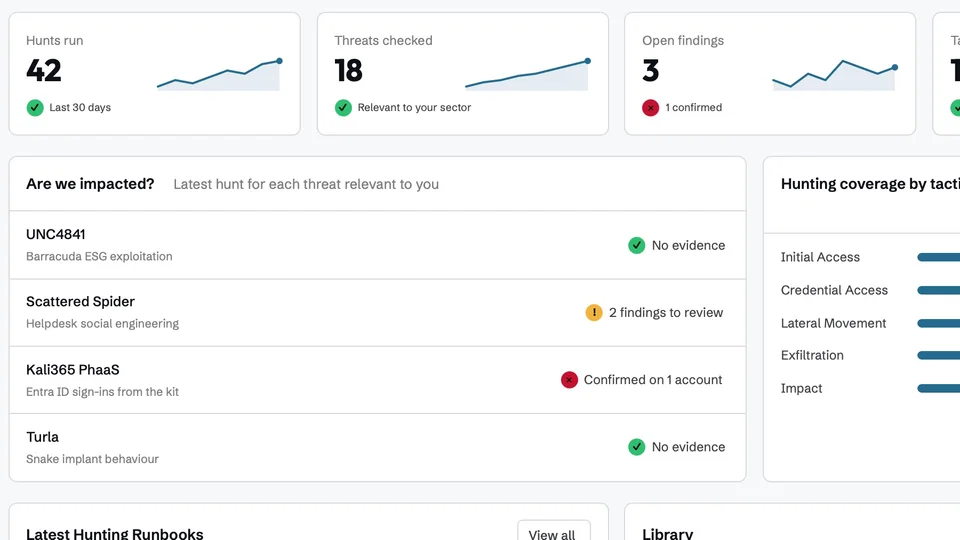
A new adversary technique becomes a runnable simulation and a hunt query within three days.
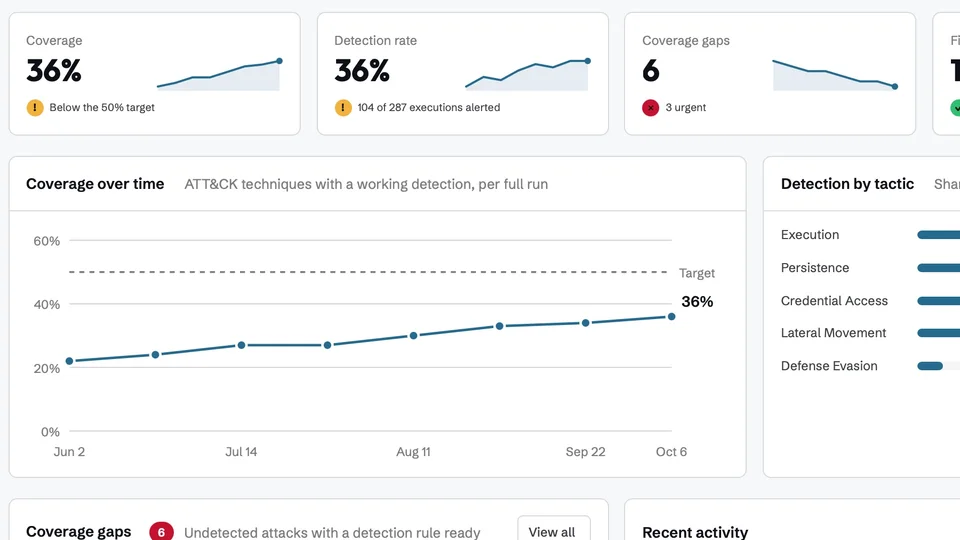
See which detections fired, which stayed silent, and what telemetry was actually captured.
Every run produces deployable detection and response logic, not a PDF of findings.
Re-run the same scenario once the fix ships and prove the gap is closed.
Every scenario mapped, so coverage is a picture you can point at.
Deploy it where your data is allowed to be.
AI-Powered
The hard part of validation is not running attacks but reading the results. Most platforms execute attacks and dump raw output with no usable analysis. The C7 Attack AI layer parses simulation results, maps detected vs. missed behaviors, and generates actionable detection rules automatically. Less noise, more signal, faster Purple Team cycles.
FAQ
C7 Attack is Crimson7's Detection & Response-as-Code (Dac & RaC) platform that automates security testing, detection development, and response orchestration through code-driven workflows.
C7 Attack focuses on security testing and detection engineering automation, while traditional SOAR platforms focus on incident response. C7 Attack treats detection and response as code, enabling version control, testing, and continuous validation and improvement.
C7 Attack supports Python, PowerShell, Bash, and custom integrations through APIs. Workflows are defined using a declarative YAML syntax with embedded code execution capabilities.
Yes. C7 Attack integrates with popular SIEM platforms, EDR solutions, threat intelligence feeds, ticketing systems, and communication tools through pre-built connectors and APIs.
Platform installation, workflow templates, integration setup, analyst training, documentation, and ongoing support. We provide starter workflows for common use cases.
C7 Attack includes built-in safety controls, testing environments, approval workflows, and rollback capabilities. All workflows undergo validation before production deployment.
Absolutely. C7 Attack's automation capabilities actually provide more value for smaller teams by reducing manual work and ensuring consistent execution of security processes.
Threat hunting queries, detection rule testing, incident triage, evidence collection, threat intelligence enrichment, vulnerability assessment, and response orchestration.
C7 Attack is licensed annually based on organization size and feature requirements. Includes platform access, updates, support, and a library of pre-built workflows.
24/7 technical support, workflow development assistance, quarterly optimization reviews, access to our workflow library, and priority feature requests.
Licensing
C7 Attack and C7 Hunt ship in three tiers. Start with Community for learning and research, run Enterprise against your own environment, or partner with us as a Service Provider. Every tier runs as SaaS or customer-hosted.
On application
For students, educators, and researchers. Learn on real community playbooks and attack scenarios, with limited seats. Access is granted on application.
Price on request
For direct customers managing their own environment, or that prefer we manage it for them. Full features with unlimited seats.
Price on request
For MSSPs, MDRs, MSPs, and managed security teams serving multiple clients.
Book a demo
See how C7 Attack delivers continuous threat validation with operator-grade depth.