Download the checklist
Five pages, free. Tell us where to send it and the download opens immediately.
By submitting, you agree to receive the checklist and follow-up notes from Crimson7. See our privacy policy.
Ten points in four sections
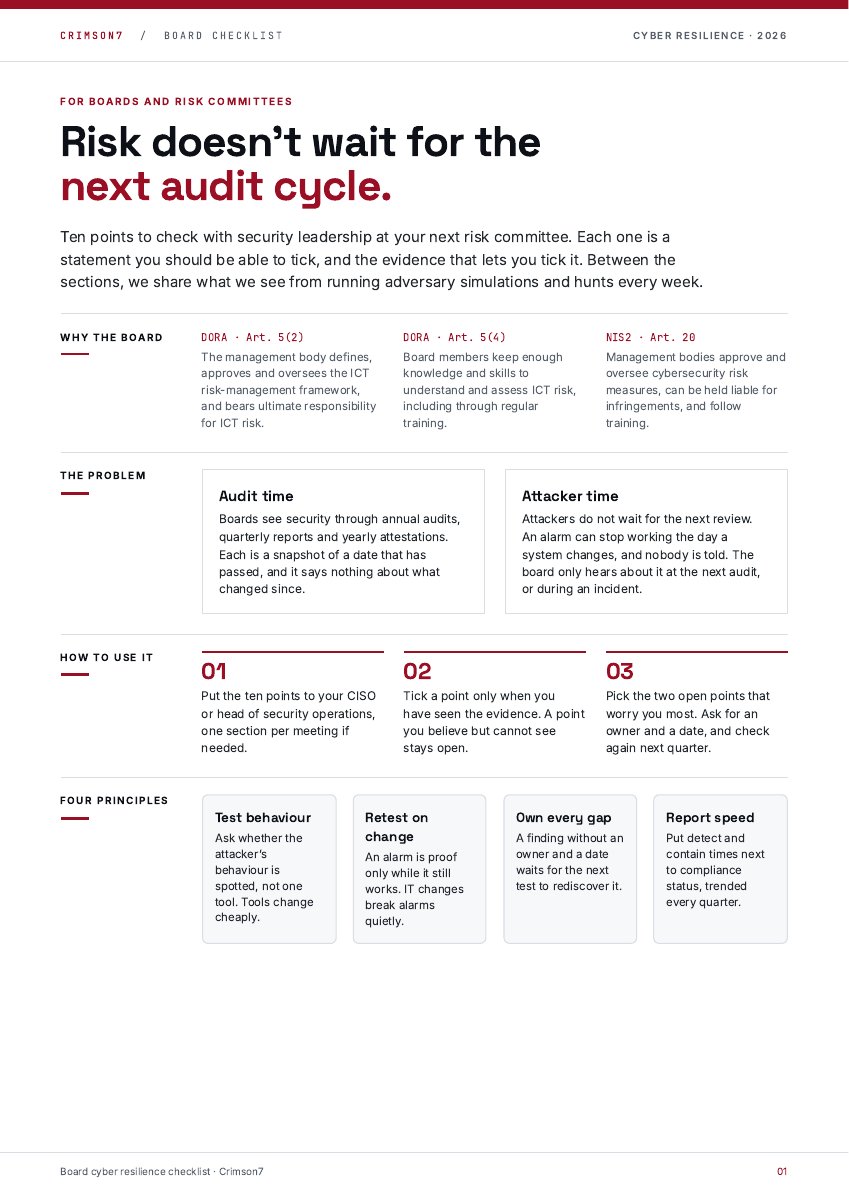
Every point explains why it matters and names the evidence a board member can ask to see. Between the sections, we share what we see from running adversary simulations and hunts every week.
Coverage
Are we tested against the attackers who target us?
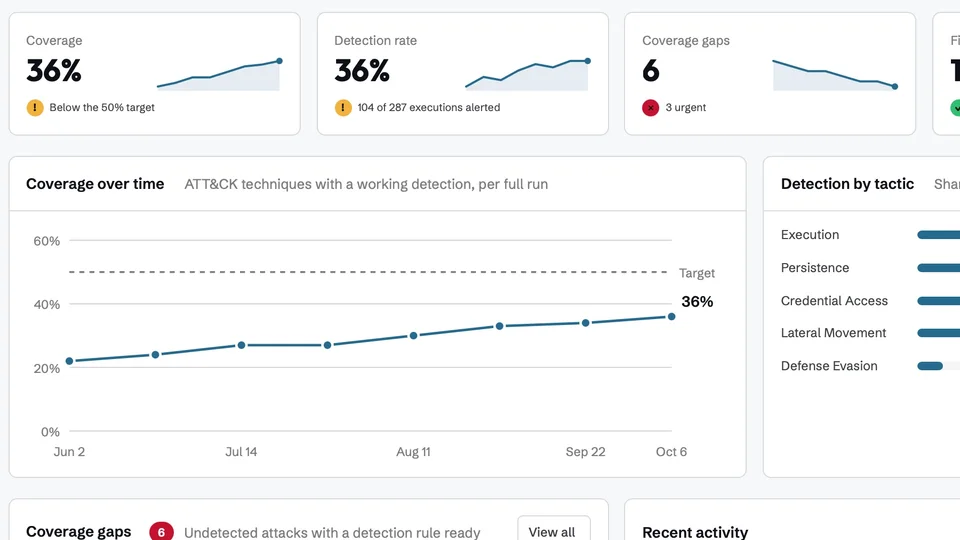
Three points on testing against the threat groups that target your sector, results per attacker level, and alarms proven in the last 90 days.
Detection speed
How fast do we notice someone is already inside?
Two points on the time it takes to spot a serious attack, and how quickly a newly reported attack method is covered.
Signal quality
Do our alerts still lead to action?
Two points on false alarms against real incidents, and retesting the alarms that an IT change could switch off.
Response and evidence
Who closes the gap, how fast, and can we prove it?
Three points on containment time, an owner and a date for every weakness, and evidence a supervisor can see today.
It closes with what to do this week, this quarter and this year, and a one-page board view of four measures to trend every quarter.
For the people who answer for cyber risk
Board members and risk committees
DORA and NIS2 make the management body responsible for ICT risk. Each point is a statement you should be able to tick, and the evidence that lets you tick it.
CISOs reporting to the board
Use it to prepare your next risk committee. It shows which evidence the board will ask for, and the four measures worth trending every quarter.
Risk, audit and compliance leads
Each point names the evidence to request, from the last test date of a critical alarm to the open weaknesses with an owner and a fix date.
See the evidence for yourself
In a demo we run real attacker behaviour against live defences and show what fires, what stays silent, and how each gap closes with a tested fix.