Download the whitepaper
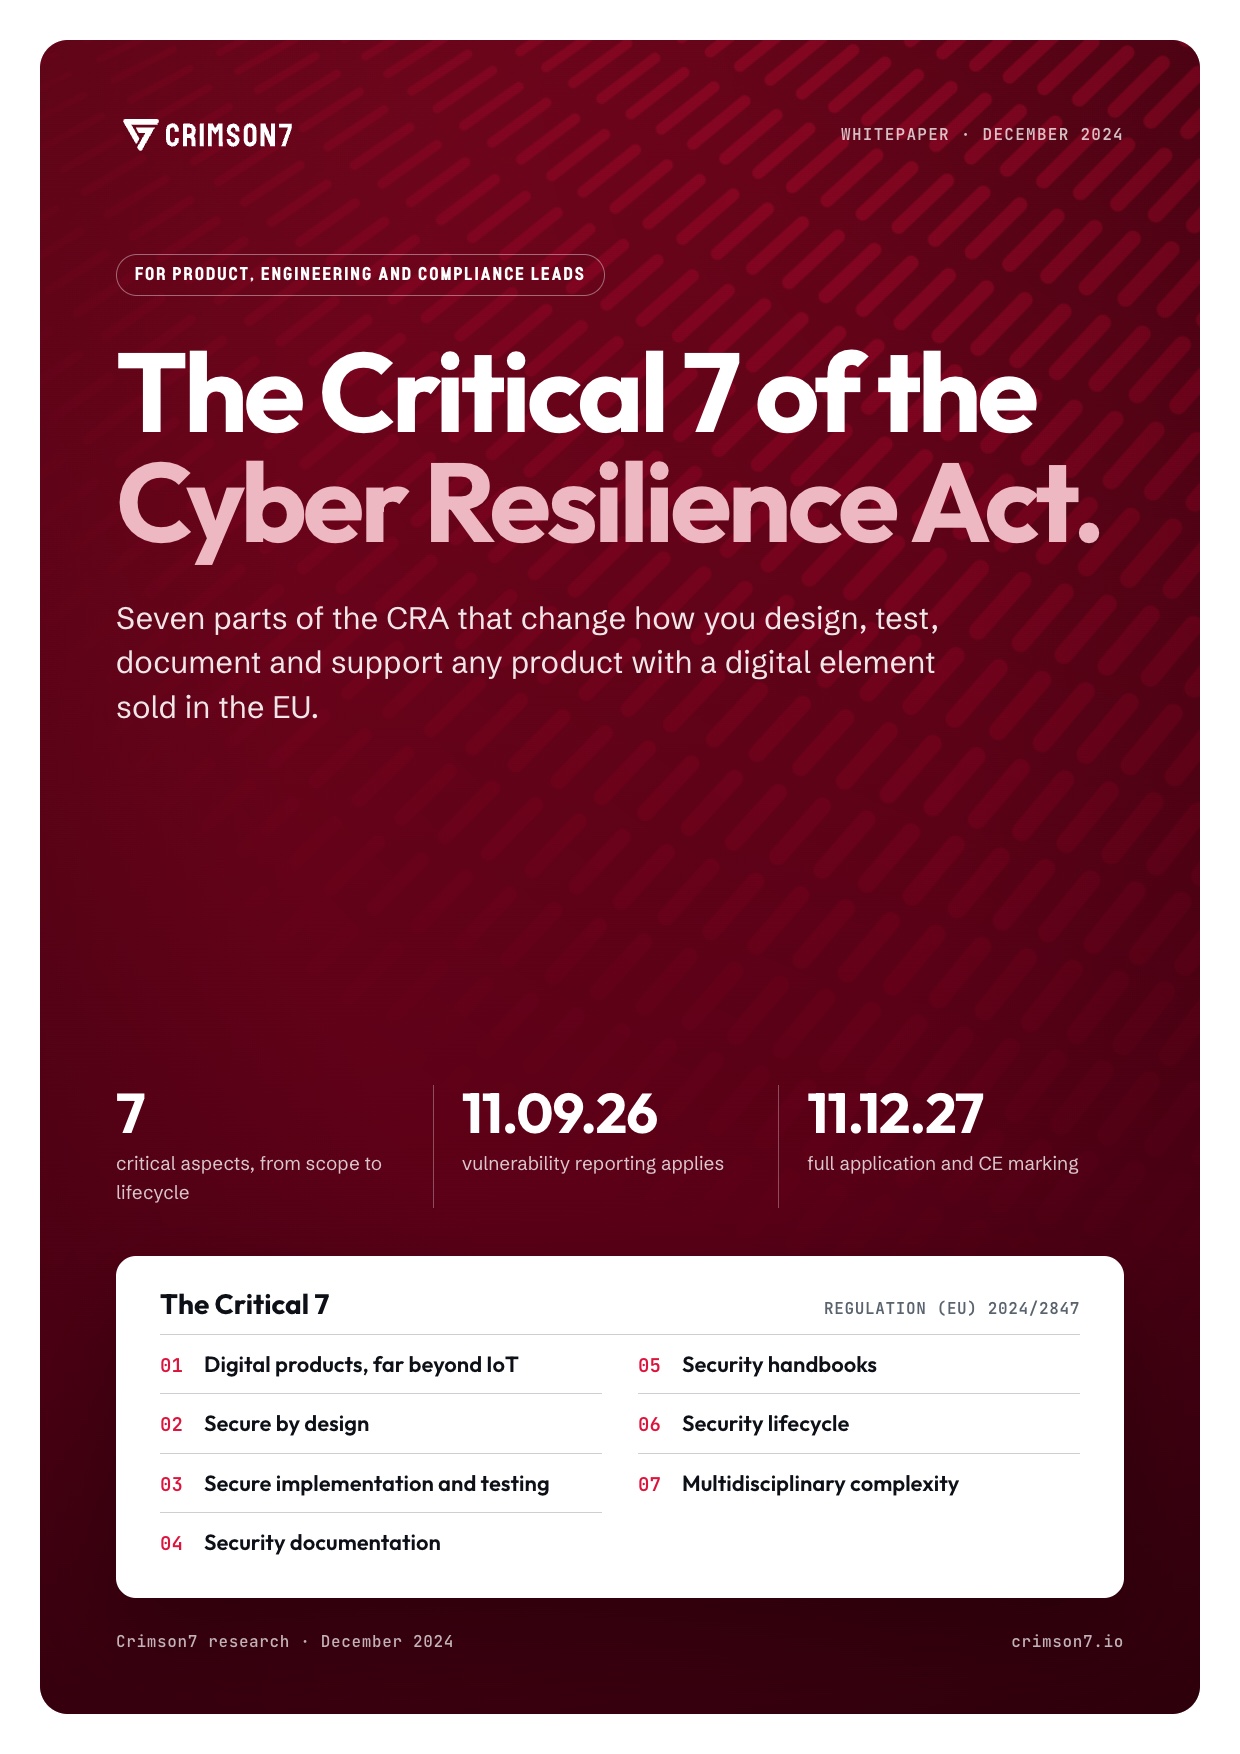
Eleven pages, free. Tell us where to send it and the download opens immediately.
By submitting, you agree to receive the whitepaper and follow-up notes from Crimson7. See our privacy policy.
Seven aspects, from scope to lifecycle
Each aspect comes with the relevant articles and annexes of Regulation (EU) 2024/2847, and what we’d do about it from testing hardware, firmware and connected products in our own lab.
Far beyond IoT
Any product with digital elements and a data connection is in scope, from accounting software to a programmable logic controller (Art. 2).
Secure by design
A risk assessment drives the design, and Annex I lists what it has to cover, from secure defaults to secure updates (Art. 13).
Implementation and testing
No known exploitable vulnerabilities at release, and effective, regular security testing of the whole system (Annex I).
Security documentation
Technical documentation that proves each requirement, including a machine-readable software bill of materials (Art. 31).
Security handbooks
What users must be told: the intended environment, updates, the support period and how to decommission the product (Annex II).
Security lifecycle
Vulnerability handling for at least five years, coordinated disclosure, and reporting of actively exploited vulnerabilities within 24 hours (Art. 13(8), Art. 14).
Legal and technical together
The CRA sits next to GDPR, NIS2 and the AI Act. Getting a product to market needs counsel and specialists from the first design review.
It closes with the key dates, a handbook checklist and three moves to start with. General guidance, not legal advice.
For anyone who releases digital products in the EU
Product leads
Without the CE marking, a product can’t be sold in the EU. See which of your products are in scope and what the support period commits you to.
Engineering leads
The Annex I requirements in plain words, with what we’d do about each one, from threat modelling to firmware and update-chain testing.
Compliance and legal leads
The articles and annexes that matter, the key dates, and the documentation and handbook a conformity assessment will ask for.
Check your product against the CRA before the regulator does
From threat model to hardware, firmware and back-end testing, we’ll walk you through how we’d approach your product.