Fragmented Workflows
Queries scattered across wikis, Slack channels, personal notes, and shared drives. No single source of truth for your hunting library.
How it works
Five stages, each in the product: start from the threat, pick the query, run the hunt, investigate with Hunter AI and report what you found.
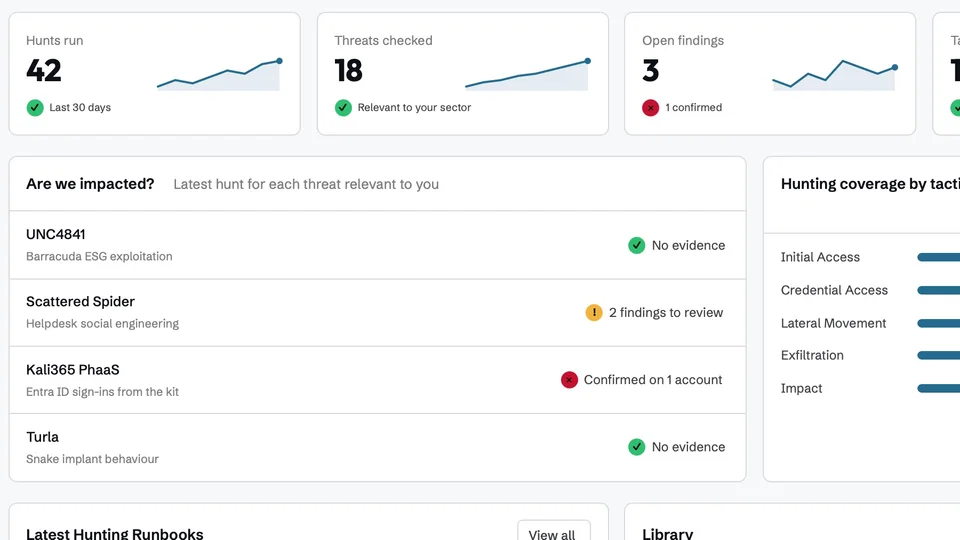
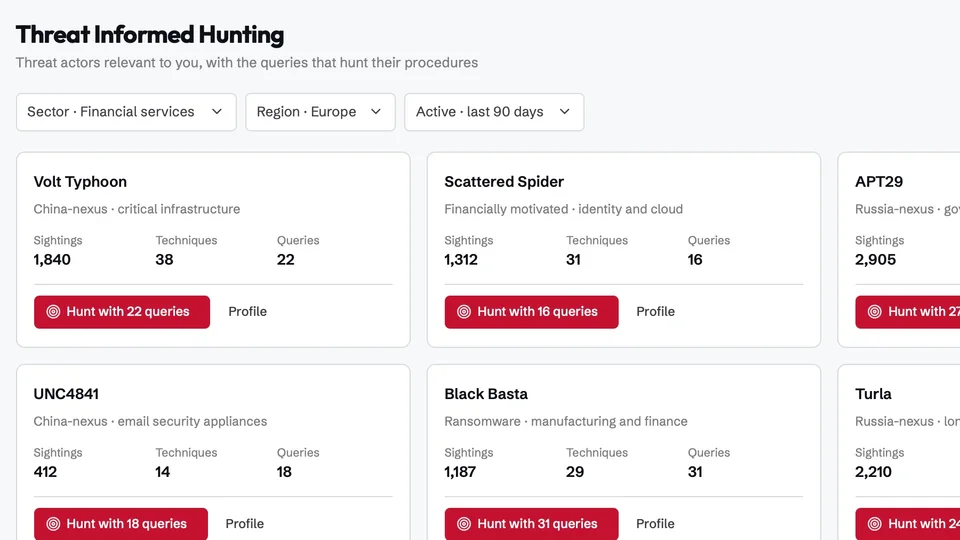
Actors targeting your sector and region, each with ready hunting queries.
A new CTI lead becomes a hunt in minutes, not weeks.
Continuous loop: new intel starts the next hunt
Book a demo
In 30 minutes an engineer runs C7 Hunt on a working environment and answers your questions on deployment, integrations and licensing. What we cover:
The Problem
Queries scattered across wikis, Slack channels, personal notes, and shared drives. No single source of truth for your hunting library.
CTI reports pile up but never become active hunts. The gap between knowing about a threat and hunting for it is weeks, not minutes.
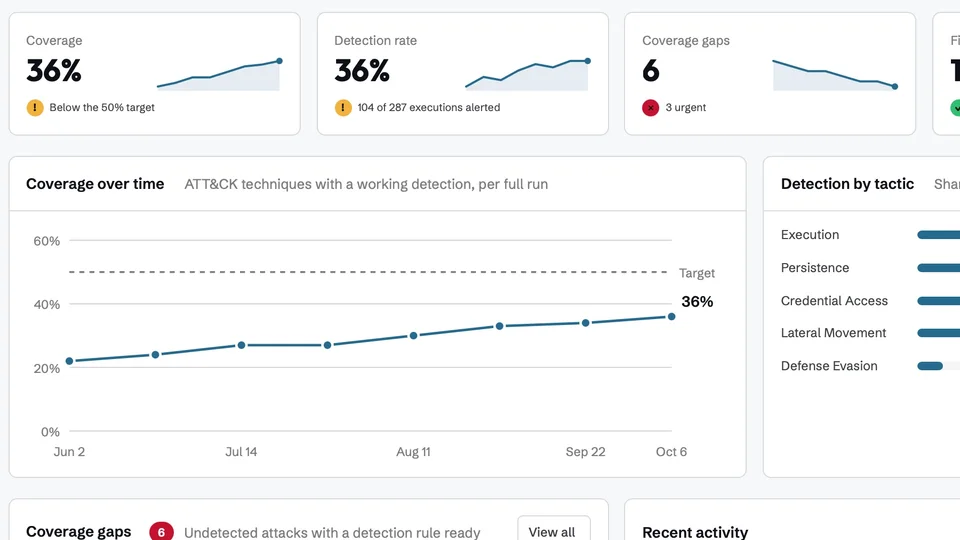
No visibility into which MITRE ATT&CK techniques you can actually detect. SOC managers can't report on hunting posture with confidence.
The Solution
C7 Hunt centralizes your threat hunting queries, investigation runbooks, and MITRE ATT&CK coverage mapping. One-click export to Microsoft Sentinel, a public REST API for SOAR integration, and data-driven visibility into your hunting posture.
Runs as fully managed SaaS or customer-hosted, with customer-selected SIEM and EDR connections. See how the platform runs in controlled environments.
Capabilities
Start from a CTI lead or a hypothesis and reach an executable hunt in minutes.
Search what is happening now and what already passed through your telemetry.
Queries, hunts and investigations in one workflow instead of scattered notebooks.
Turn what two people know into a procedure the whole team can run.
One place for hunts, investigations and coverage, so nothing lives only in someone's head.
Report coverage per hunt, so every engagement ends with a defensible picture.
Run live queries mid-investigation so iteration does not stall on syntax.
The hunt is created for you in Sentinel, not copied by hand.
Wire hunts into SOAR pipelines and existing automation.
AI-Powered
The C7 Hunt AI assistant doesn't just suggest queries, it can execute live KQL queries during investigations. Ask it to hunt for specific indicators, build custom queries on the fly, or walk you through a runbook step by step. Real-time threat hunting, powered by intelligence.
FAQ
C7 Hunt is Crimson7's advanced threat hunting platform that combines automated hunting queries, behavioral analytics, and expert-curated threat intelligence to identify sophisticated threats.
C7 Hunt focuses on proactive threat hunting and hypothesis-driven investigation, while EDR focuses on endpoint detection and response. C7 Hunt operates across your entire security stack, not just endpoints.
Network traffic, endpoint logs, cloud infrastructure events, email security data, identity events, vulnerability scans, and threat intelligence feeds. C7 Hunt normalizes data across multiple sources.
Both. C7 Hunt includes the platform plus managed threat hunting services from our expert analysts. You can also use the platform independently with training.
Our threat intelligence combines commercial feeds, open source intelligence, dark web monitoring, and insights from our red team engagements. It's specifically curated for hunting scenarios.
C7 Hunt typically identifies threats within hours rather than days or months. Continuous analysis and behavioral modeling enable rapid detection of subtle indicators.
MITRE ATT&CK-mapped queries, APT group behavioral patterns, living-off-the-land technique detection, supply chain compromise indicators, and custom queries based on current threat landscape.
Yes. C7 Hunt integrates with major SIEM platforms including Sentinel, Splunk, Elastic, and QRadar. It can also operate as a standalone hunting platform.
Comprehensive threat hunting methodology training, platform usage sessions, custom query development workshops, and ongoing education on emerging threats and techniques.
We track threat detection metrics, time-to-discovery, investigation efficiency, false positive rates, and coverage across MITRE ATT&CK framework. Regular reporting provides visibility into hunting program maturity.
C7 Hunt can be deployed on-premises, in your cloud environment, or as a hybrid solution. We work with your infrastructure requirements and compliance needs.
Yes. Detailed hunting reports include threat findings, intelligence insights, recommended actions, and trending analysis. Executive summaries are provided for leadership visibility.
Licensing
C7 Attack and C7 Hunt ship in three tiers. Start with Community for learning and research, run Enterprise against your own environment, or partner with us as a Service Provider. Every tier runs as SaaS or customer-hosted.
On application
For students, educators, and researchers. Learn on real community playbooks and attack scenarios, with limited seats. Access is granted on application.
Price on request
For direct customers managing their own environment, or that prefer we manage it for them. Full features with unlimited seats.
Price on request
For MSSPs, MDRs, MSPs, and managed security teams serving multiple clients.
Book a demo
See how C7 Hunt can centralize your hunting operations and give your SOC data-driven visibility into threat coverage.